On-Premise DAST for Sensitive and Isolated Environments
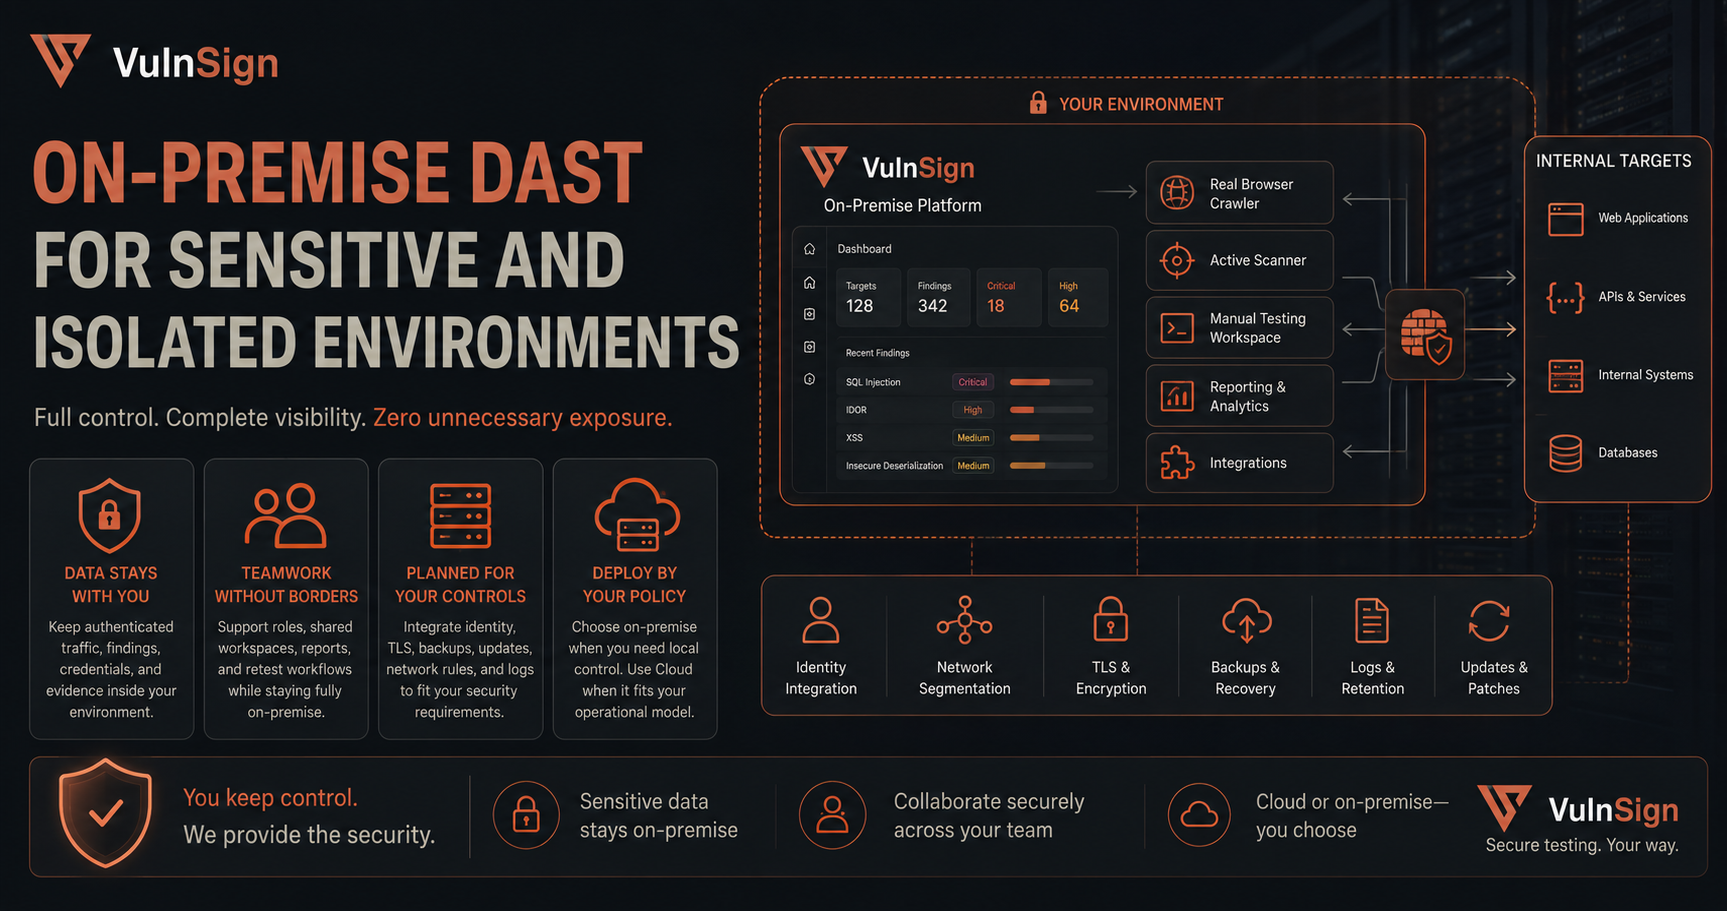
Security testing handles sensitive data
Authenticated traffic, credentials, internal routes, vulnerability evidence, and remediation details require careful control. An on-premise platform keeps the testing control plane within the organization’s selected environment.
Local does not mean disconnected work
A locally managed deployment can still support authorized browser access, team roles, shared findings, reporting, and retest workflows. The goal is to keep collaboration while respecting network segmentation and data-residency requirements.
Plan the surrounding controls
Define identity integration, TLS termination, backups, update windows, outbound access, scanner placement, and log retention before rollout. Use dedicated service accounts and ensure scan traffic reaches only approved target ranges.
Choose deployment by policy
VulnSign supports both Cloud and on-premise delivery. Teams can use managed operations where appropriate and retain local control where regulation, customer commitments, or network isolation require it.
Related Articles
Explore more insights, strategies, and perspectives related to this topic.
Questions before you scan?
Learn how VulnSign fits into your environment, security workflow, and team.
Put automated and manual testing in one workflow.
See how VulnSign helps your team discover more attack surface, validate risk, and move findings to remediation—without sending security data to a cloud control plane.