Application security, from discovery to verified remediation
Practical guidance from VulnSign Research on DAST engineering, attack-surface management, DevSecOps, and operating application security in Cloud or on-premise environments.
Cloud or On-Premise DAST: Choose the Right VulnSign Deployment
Compare operational control, data residency, scaling, and maintenance when deploying VulnSign Cloud or on-premise.
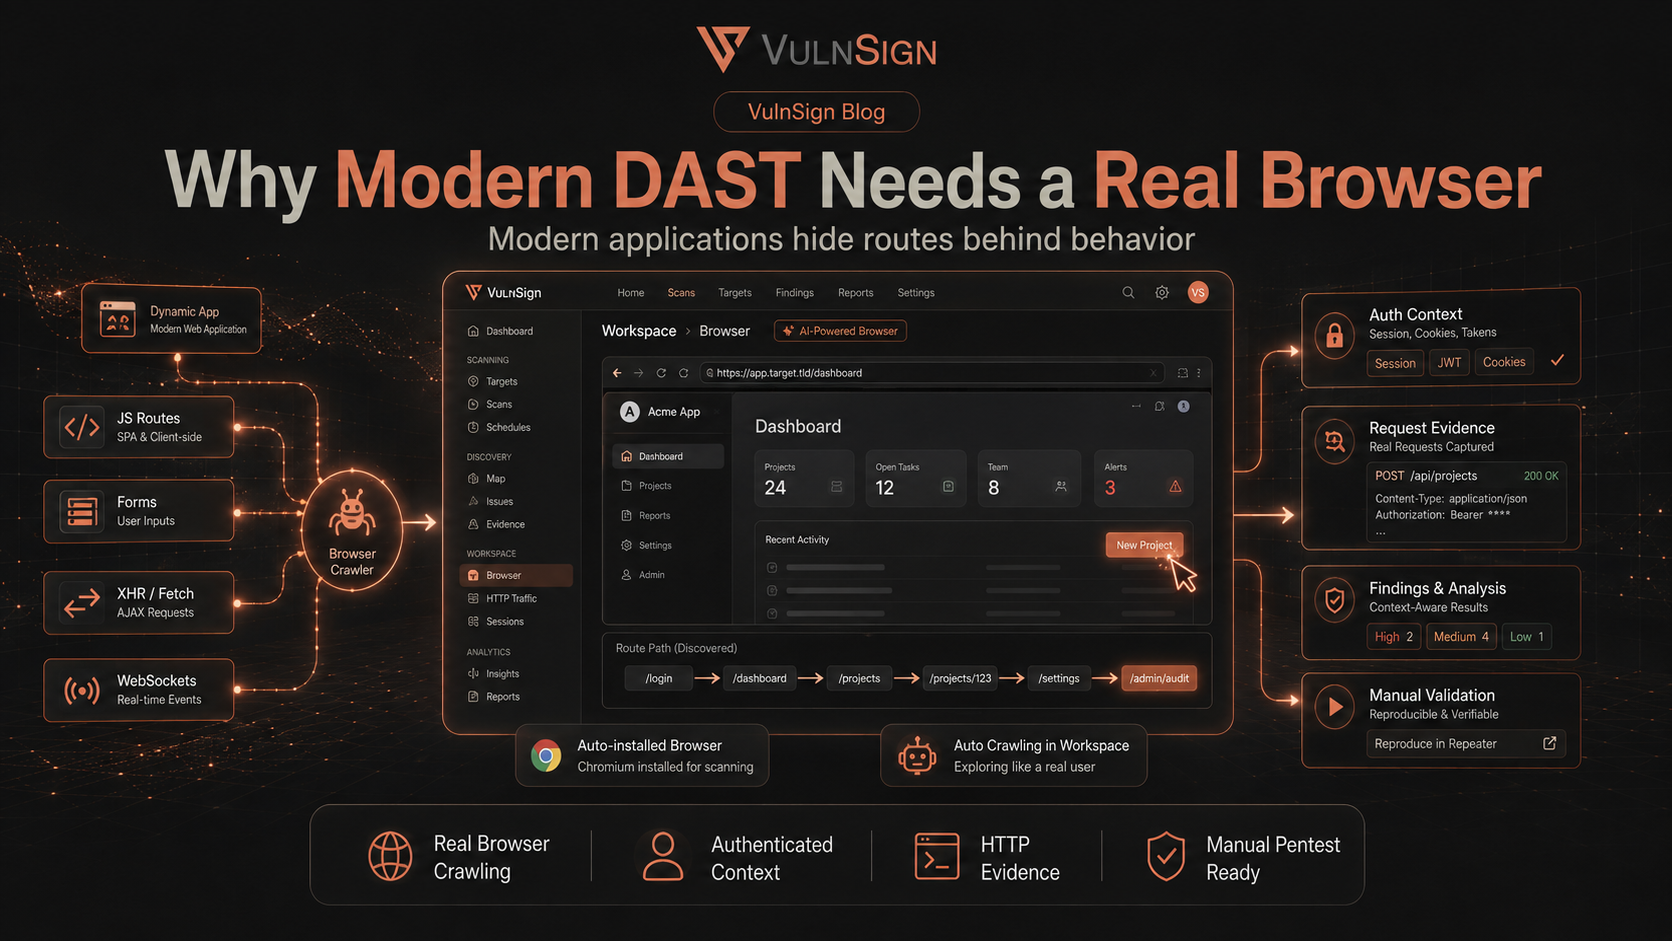
Why Modern DAST Needs a Real Browser
See how JavaScript execution, session state, and event-driven discovery reveal attack surface that link crawlers miss.
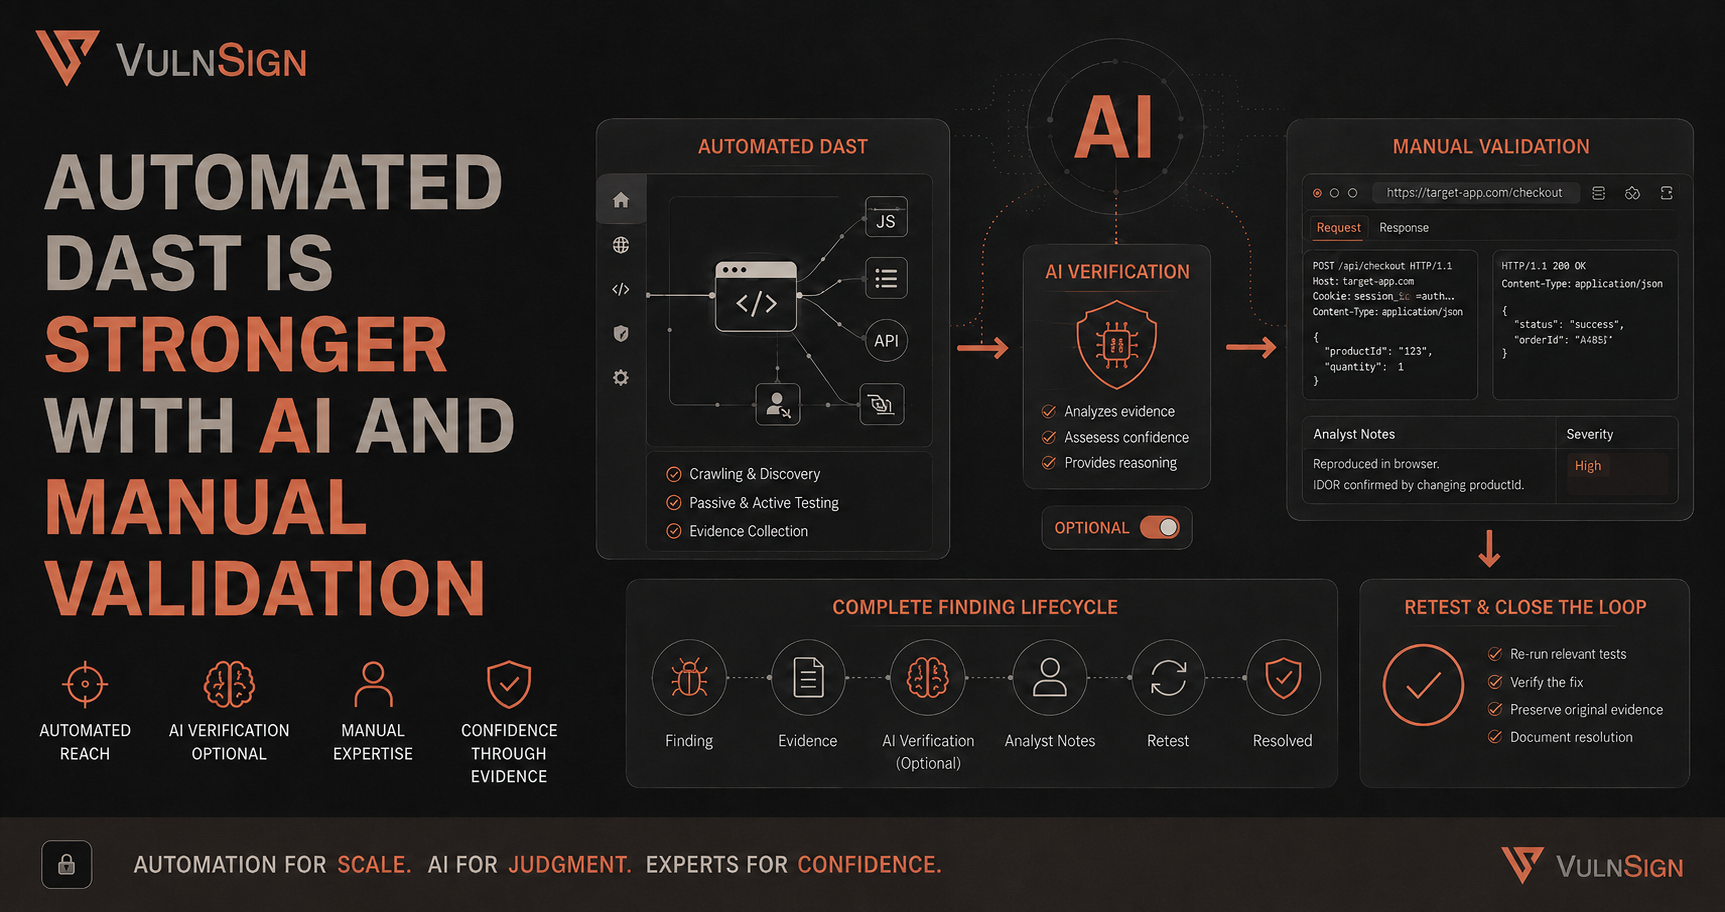
Automated DAST Is Stronger with AI and Manual Validation
Combine automated DAST with optional, model-selectable AI verification and hands-on analyst validation in one evidence-driven workflow.
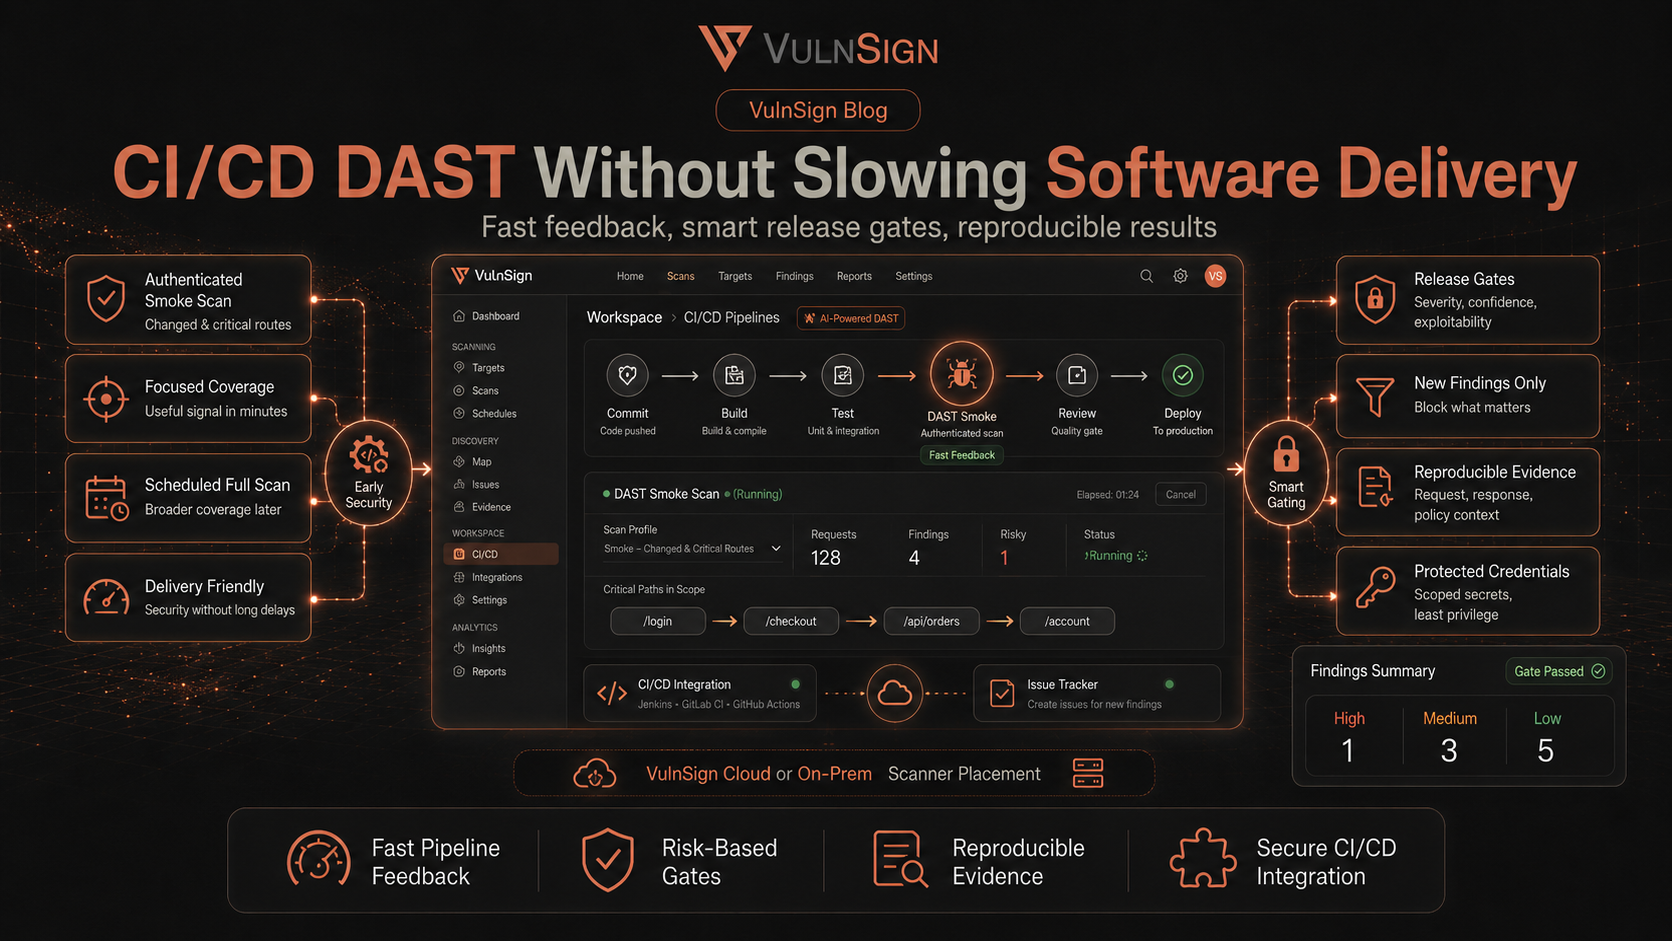
CI/CD DAST Without Slowing Software Delivery
Use risk-based policies, scheduled coverage, and actionable feedback to add DAST to delivery pipelines.
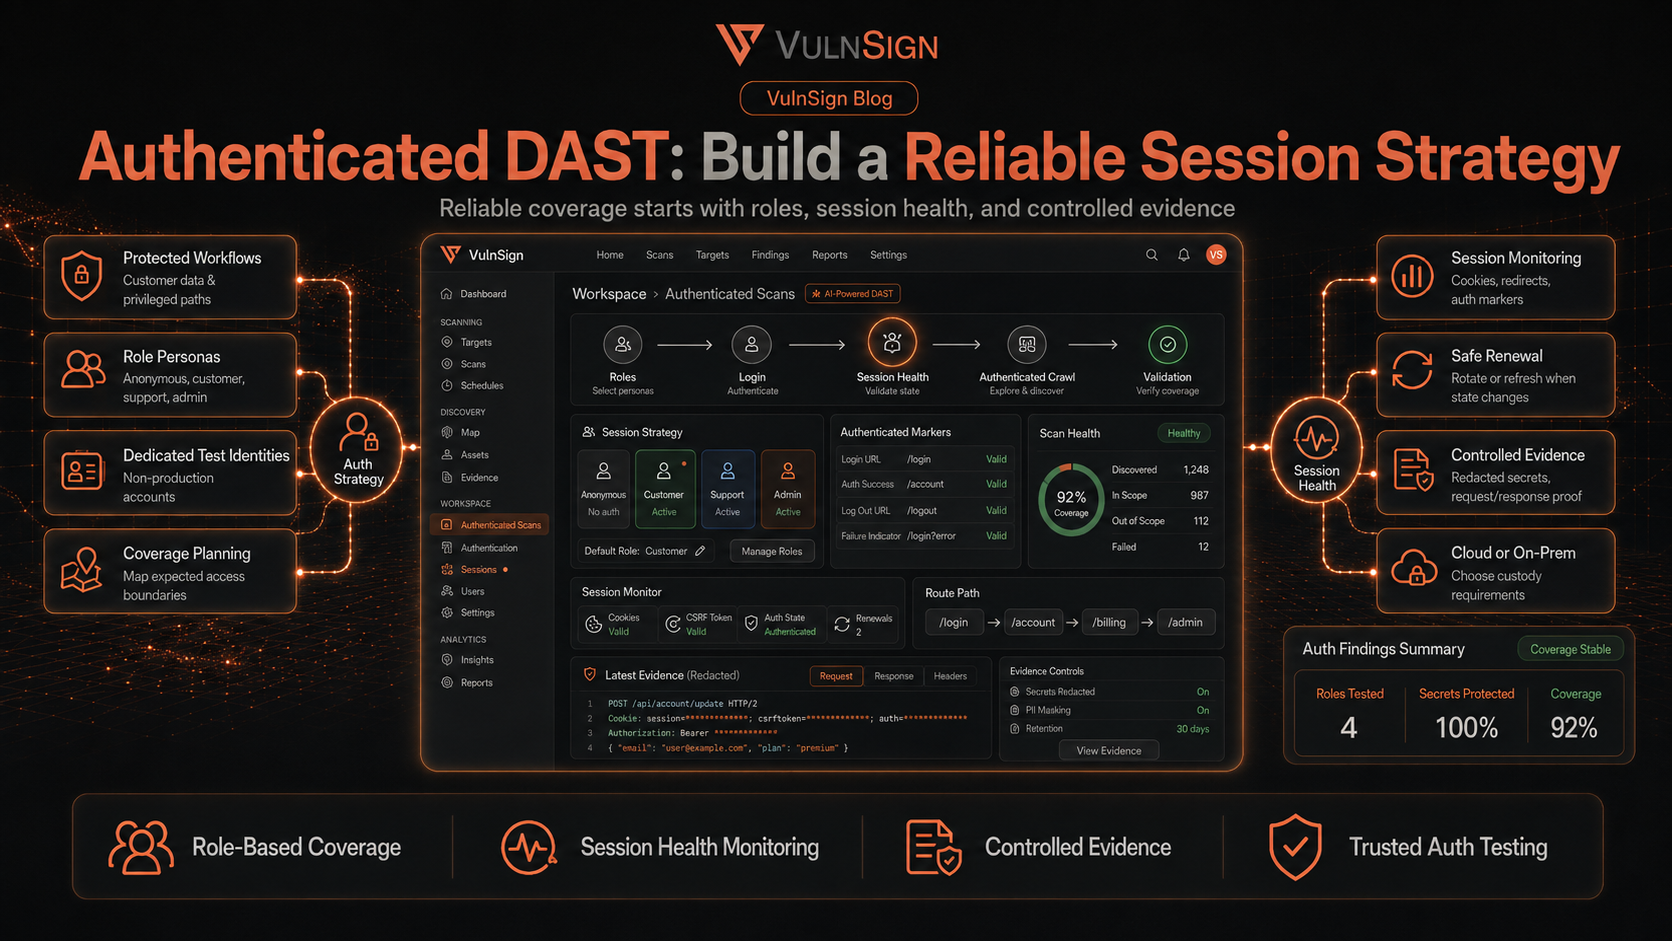
Authenticated DAST: Build a Reliable Session Strategy
Plan test identities, login flows, session renewal, and role coverage before scanning protected application paths.
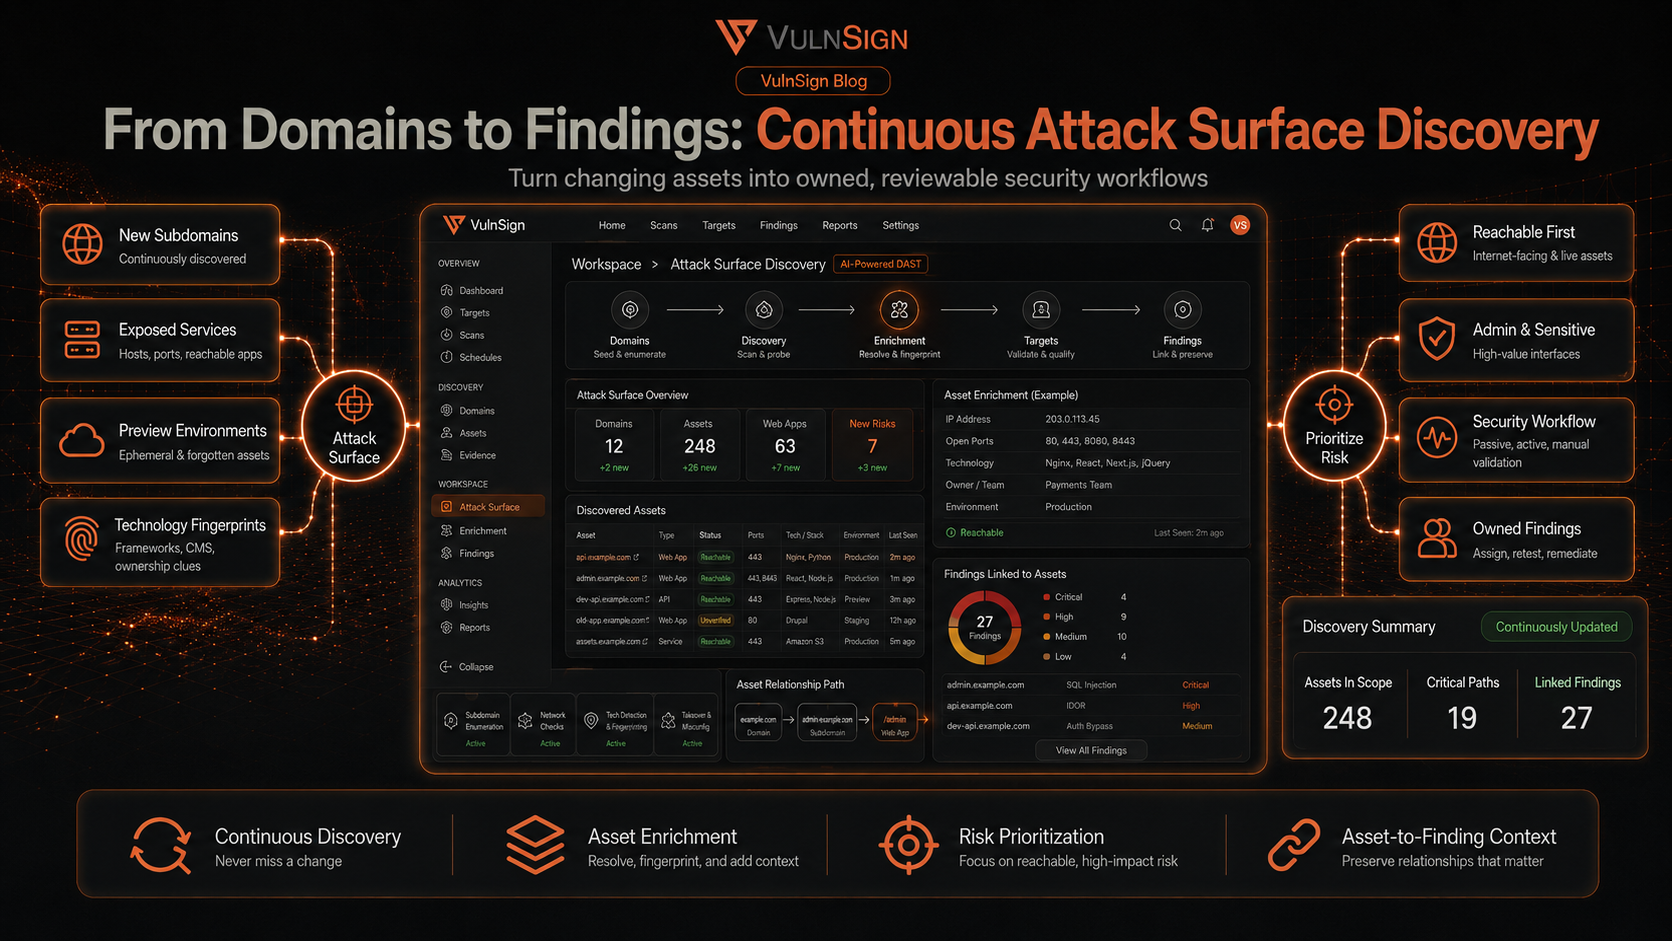
From Domains to Findings: Continuous Attack Surface Discovery
Connect subdomain enumeration, port scanning, technology detection, and web testing into one prioritized workflow.
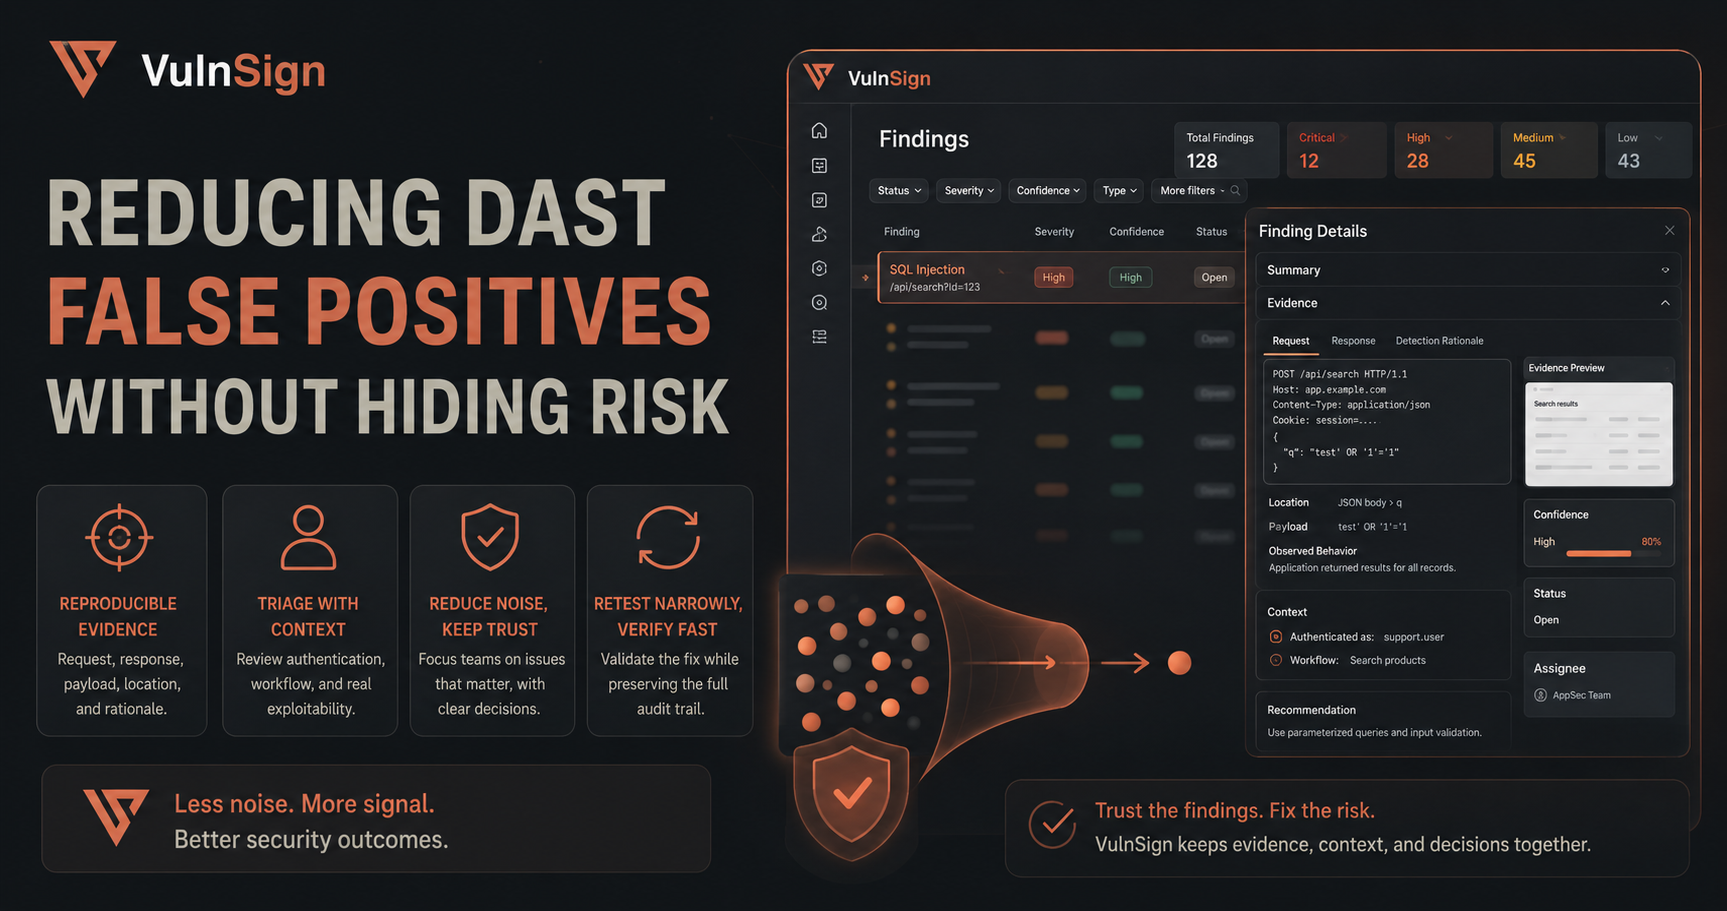
Reducing DAST False Positives Without Hiding Risk
Combine confidence, evidence, manual triage, and targeted retesting to keep vulnerability queues actionable.
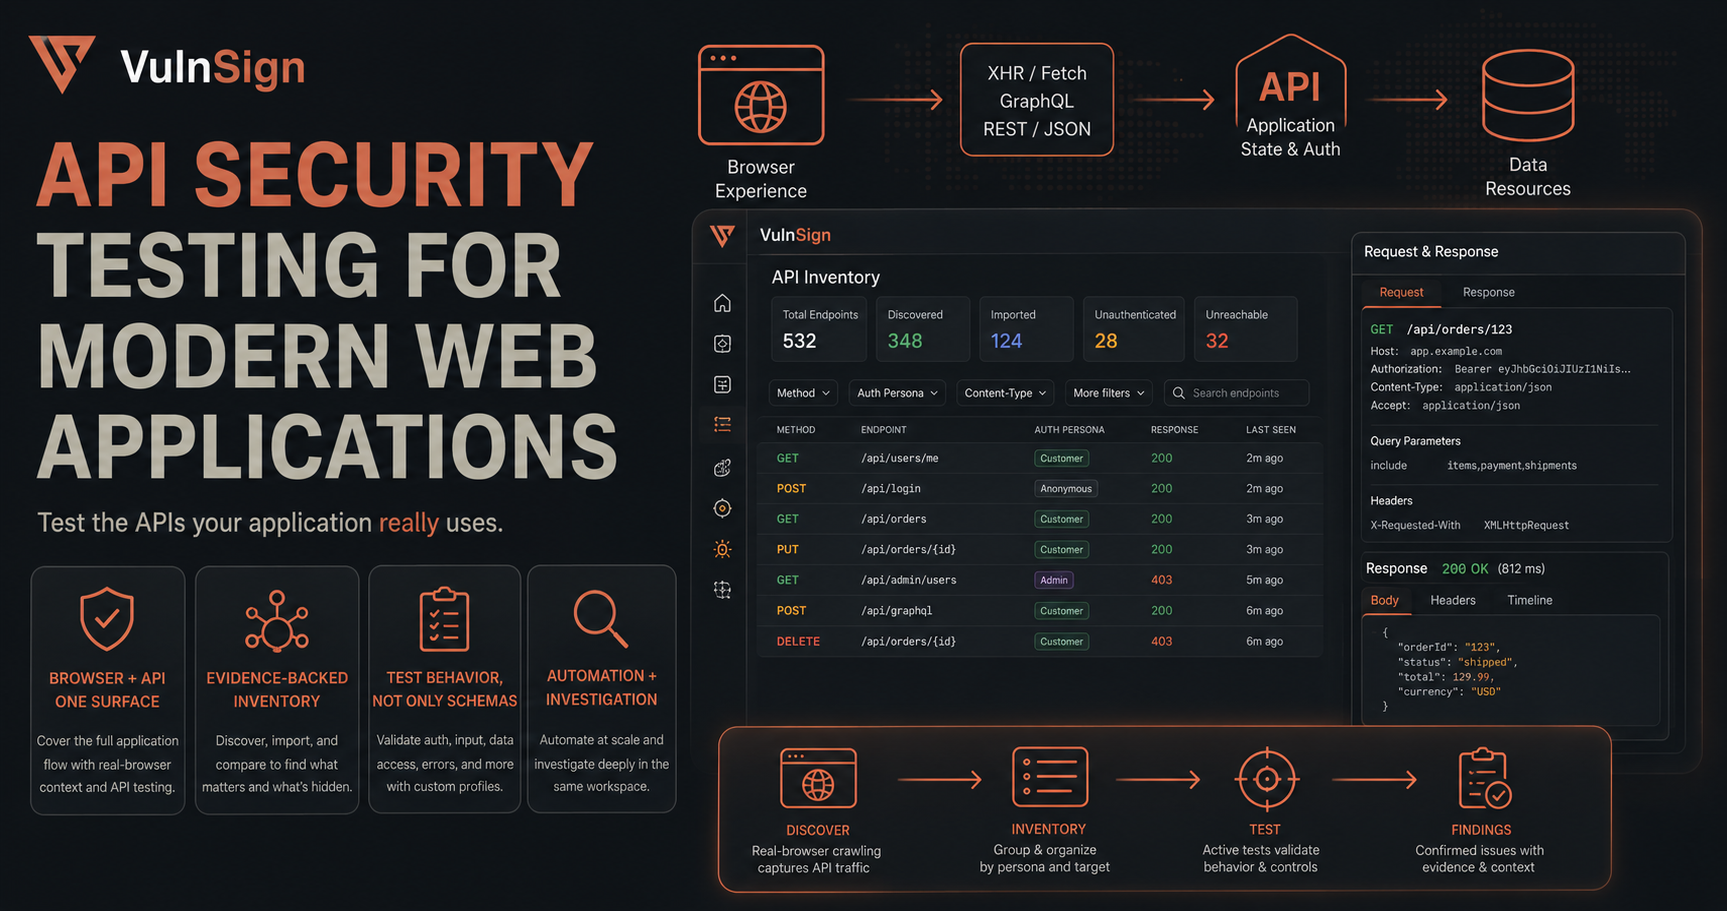
API Security Testing for Modern Web Applications
Unify browser-observed API traffic, custom payloads, authentication, and manual investigation for deeper coverage.
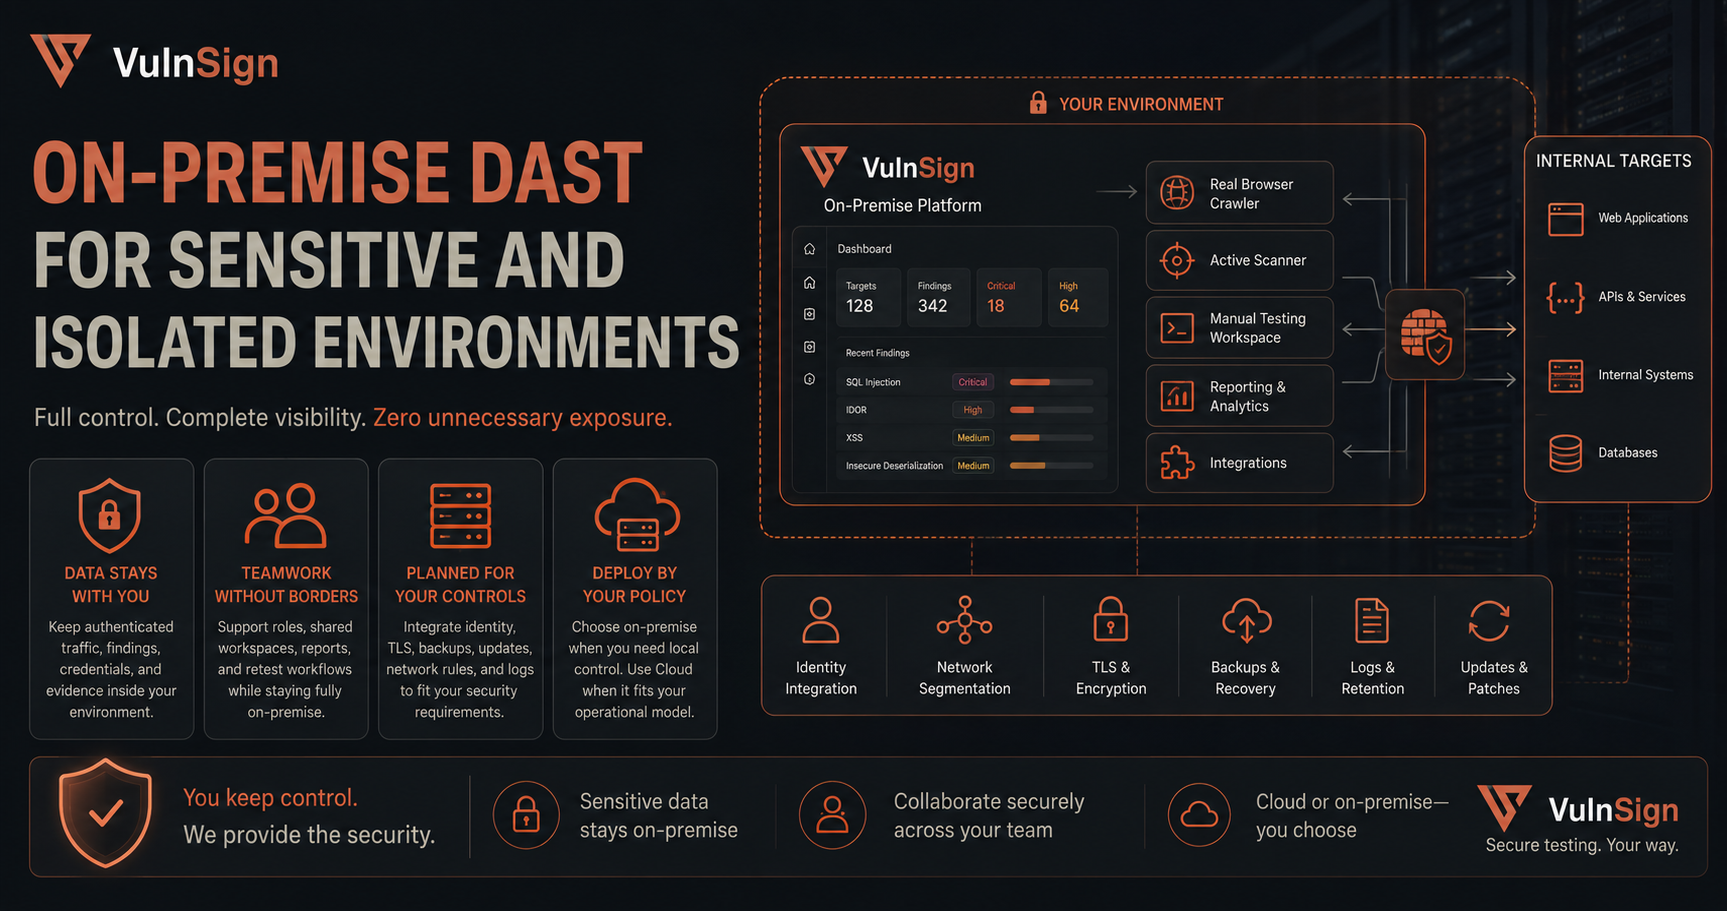
On-Premise DAST for Sensitive and Isolated Environments
Keep targets, credentials, scan traffic, findings, and evidence within infrastructure your organization controls.
Questions before you scan?
Learn how VulnSign fits into your environment, security workflow, and team.
Put automated and manual testing in one workflow.
See how VulnSign helps your team discover more attack surface, validate risk, and move findings to remediation—without sending security data to a cloud control plane.