From Domains to Findings: Continuous Attack Surface Discovery
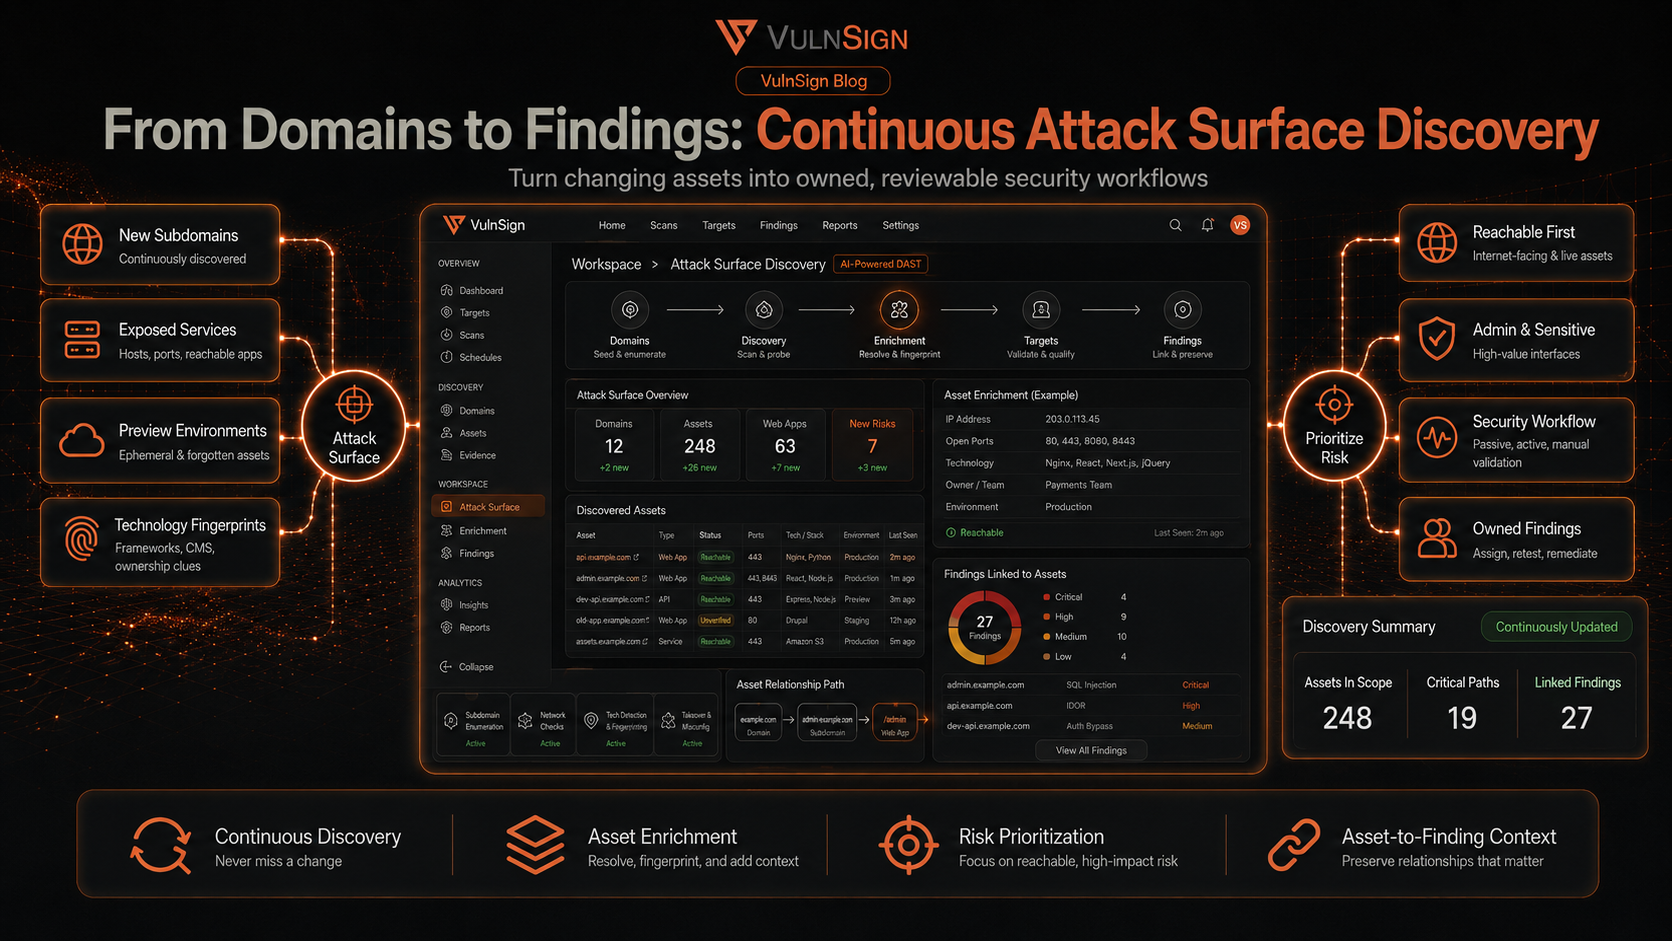
Inventory changes faster than spreadsheets
New subdomains, exposed services, preview environments, and forgotten applications appear continuously. Asset discovery becomes valuable when it feeds an owned, reviewable security workflow instead of producing another disconnected list.
Enrich before you scan
Resolve hosts, identify reachable ports, fingerprint technologies, and record ownership context. This enrichment helps teams choose an appropriate scanning policy and avoid applying invasive tests to an unknown production service.
Prioritize reachable risk
Focus first on internet-facing assets, administrative interfaces, sensitive technologies, and systems without a clear owner. Then connect discovered web services to real-browser crawling, passive analysis, active checks, and manual validation.
Preserve the asset-to-finding relationship
VulnSign combines subdomain enumeration, network checks, technology fingerprinting, targets, and findings in one workspace. That relationship makes it easier to assign ownership, track remediation, and prove that a previously exposed path was retested.
Related Articles
Explore more insights, strategies, and perspectives related to this topic.
Questions before you scan?
Learn how VulnSign fits into your environment, security workflow, and team.
Put automated and manual testing in one workflow.
See how VulnSign helps your team discover more attack surface, validate risk, and move findings to remediation—without sending security data to a cloud control plane.