Authenticated DAST: Build a Reliable Session Strategy
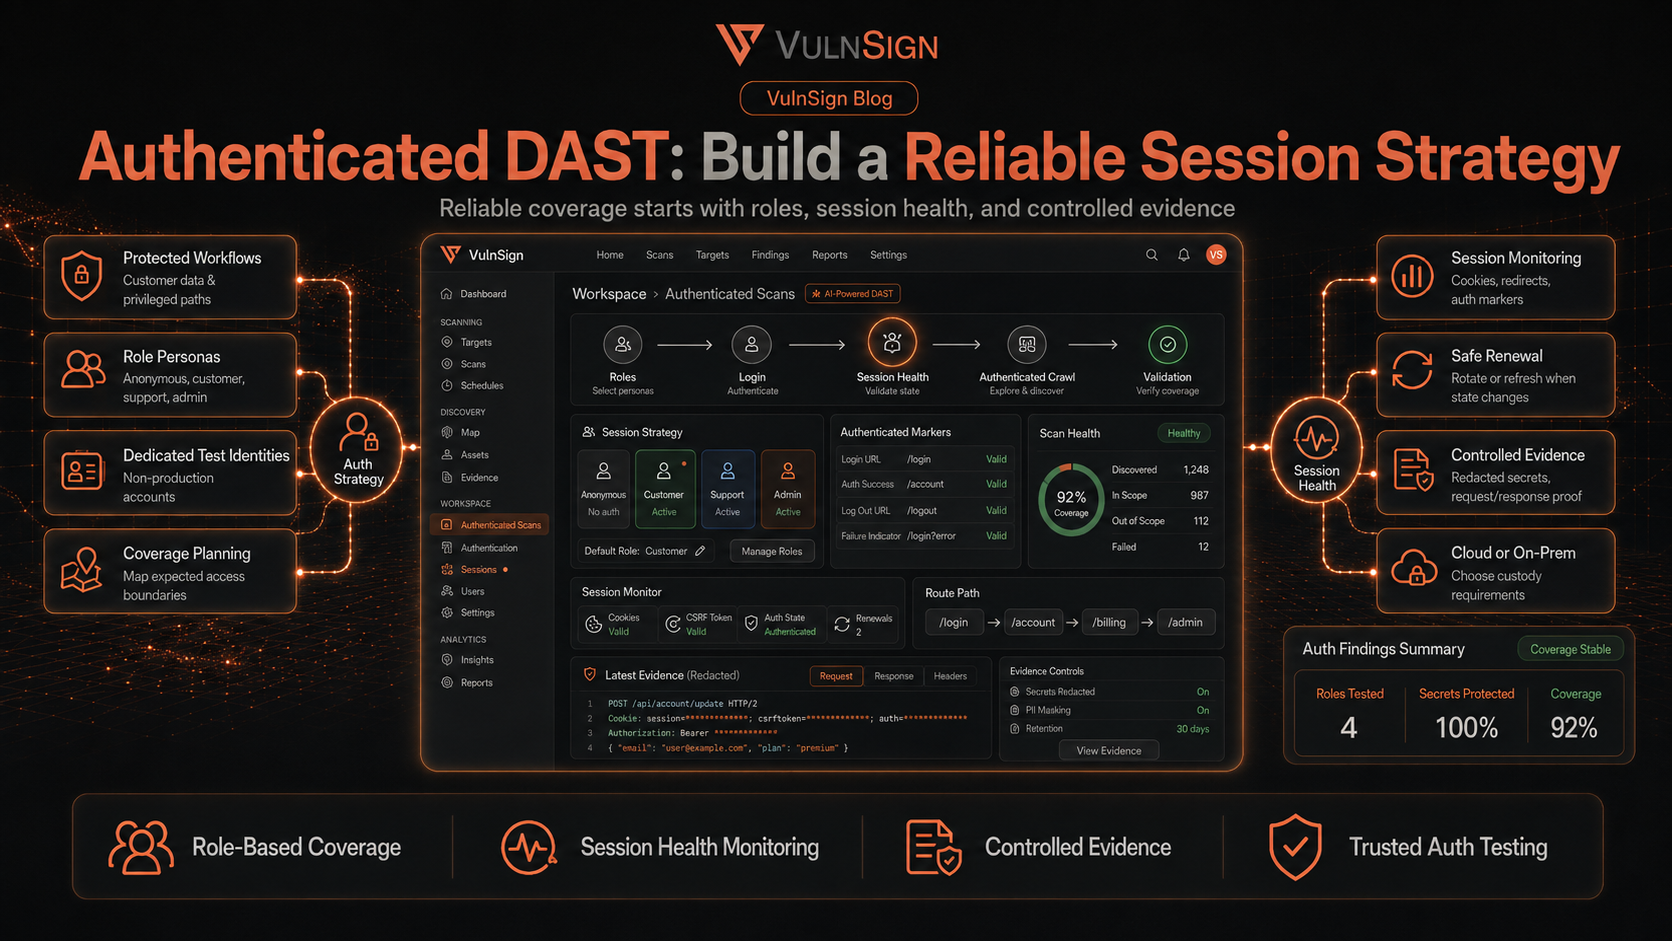
Most valuable paths are behind login
Public crawling rarely represents the workflows that process customer data or privileged actions. Authenticated DAST needs a deliberate identity strategy rather than a single username and password added at the end of scan setup.
Model personas and permissions
List the roles that expose meaningfully different routes: anonymous visitor, customer, support operator, administrator, or tenant owner. Use dedicated non-production identities and map expected access boundaries before testing.
Treat session health as a scan signal
Login success at the beginning does not guarantee authenticated coverage. Sessions expire, anti-CSRF values rotate, and applications redirect when authorization changes. Monitor authenticated markers and renew the session safely when they disappear.
Keep secrets and evidence controlled
Limit permissions, rotate test credentials, redact sensitive values in exported evidence, and choose Cloud or on-premise deployment according to custody requirements. Reliable authentication improves both coverage and the trustworthiness of every resulting finding.
Related Articles
Explore more insights, strategies, and perspectives related to this topic.
Questions before you scan?
Learn how VulnSign fits into your environment, security workflow, and team.
Put automated and manual testing in one workflow.
See how VulnSign helps your team discover more attack surface, validate risk, and move findings to remediation—without sending security data to a cloud control plane.